

ASOS Data Breach Confirmed After Rogue App Notifications
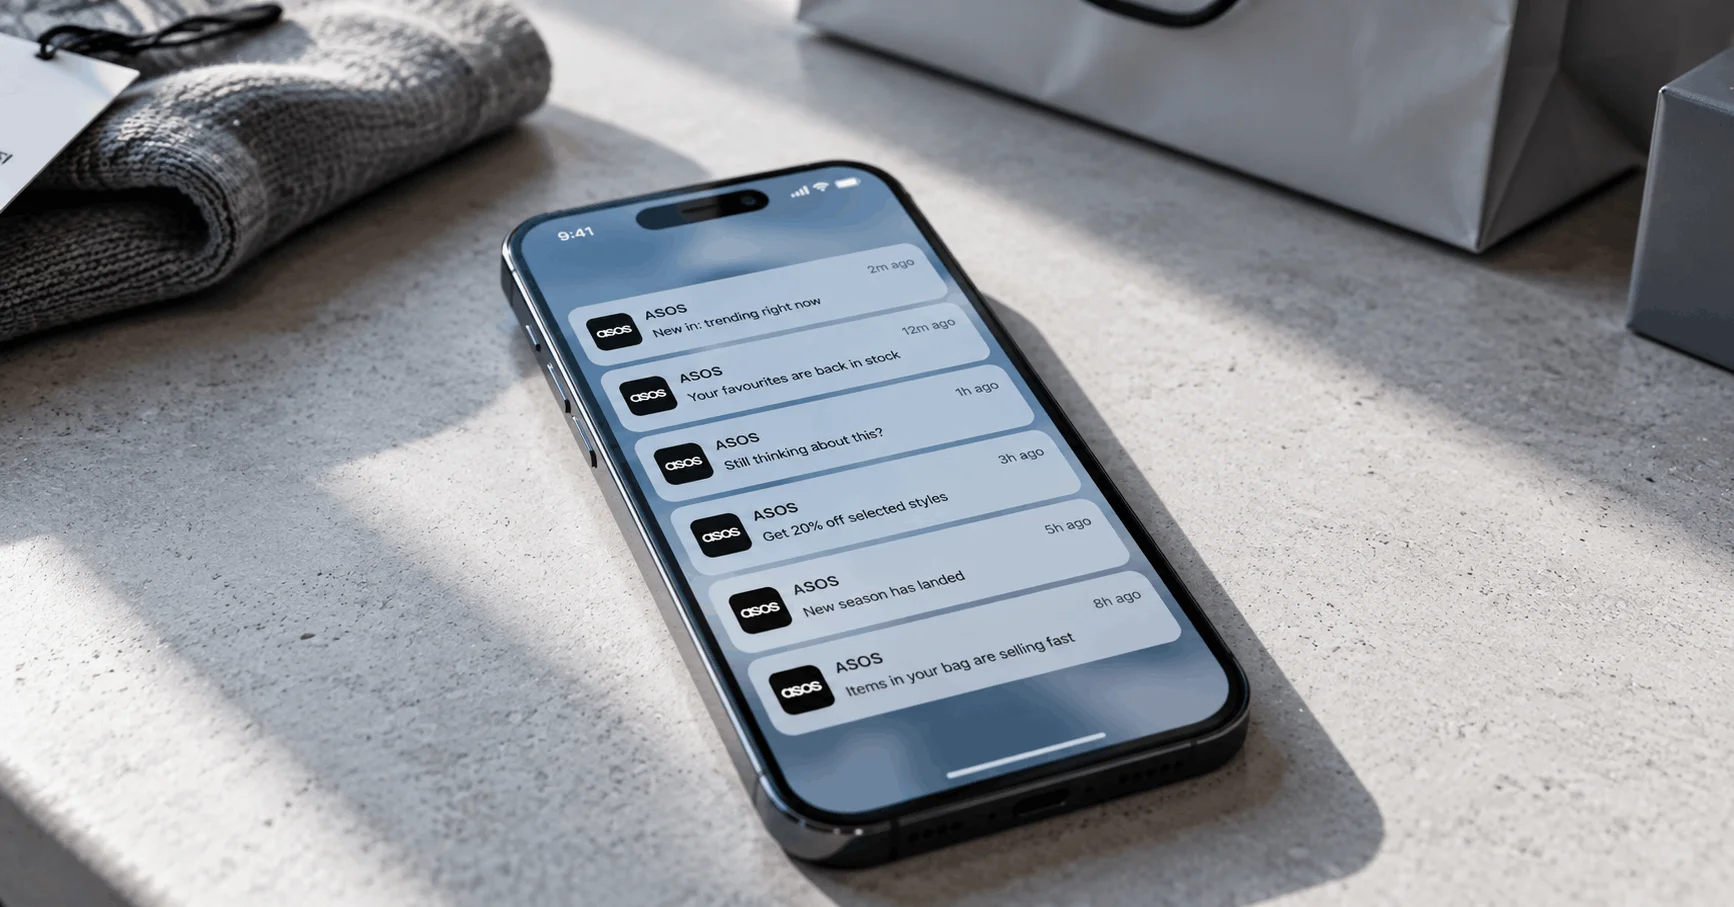
Customers of UK fashion retailer ASOS opened their phones on Tuesday to a push notification from the company's own app. It read "ASOS HACKED" and addressed the retailer's data protection officer. ASOS has since confirmed a data breach, saying attackers gained unauthorised access to the third-party platforms it uses to contact customers.
ASOS says the data breach may have exposed basic personal information, including names and contact details. It does not believe attackers reached payment card information or account passwords. The app now carries an in-app notice telling customers to disregard the unauthorised alert and to avoid the external link the message contained. ASOS has not said how many customers the data breach affected.
How the ASOS Data Breach Reached Every Phone
The notifications started arriving at roughly 5:00 a.m. ET on Tuesday. Reports piled up across social platforms within the hour. The volume suggested the alert landed on most of the user base. For a retailer with millions of app installs, that is an exceptionally wide blast radius to get out of one compromised credential.
ASOS points to third-party platforms used for customer communication as the entry point for the data breach, though it has not named the provider. Nor has it explained how attackers obtained access. Retailers route push notifications, emails and in-app messages through engagement platforms. Each platform holds an API key and a permission set covering the entire subscriber list.
So the key becomes the voice of the brand. Anyone holding it can address every customer at once, with the retailer's logo attached and the operating system's trust already granted. The message arrives looking routine. The ASOS data breach never had to touch the storefront, the checkout flow or the payment stack to land on every screen.
An Extortion Note Delivered Through the Brand's Own Channel
The notification addressed the company's data protection officer and IT team directly. It claimed full compromise of the ASOS Snowflake instance and threatened a leak unless the retailer engaged. The message also linked to a Telegram channel run by a group calling itself Xuanye, and that channel filled up through the morning. Nothing in the posts identified the people behind the name.
An early message said the data breach did not touch payment information at ASOS. The group later published what it labelled a final statement. It claims to hold customer information, says the app remains safe to use, and promises the data will sit untouched on its server for a designated period. The tone read as performative rather than negotiating.
Extortion crews normally work in private. They use encrypted messaging, a dedicated leak site, or a direct email to the security team. Pushing the demand to every customer at once inverts that model, because the audience the retailer most wants to protect learns about the problem first. The ASOS data breach became public through the retailer's own channel, before any negotiation could start.
The Snowflake Claim Behind the ASOS Data Breach
ASOS has not confirmed the Snowflake element of the data breach, and the group behind it has produced nothing to support the claim. No file samples. No record counts, and no screenshots of the environment. It has not said what customer information it holds, or how many people the alleged theft covers.
That gap matters, because the claim carries weight on reputation alone. A 2024 campaign against Snowflake customer tenants hit roughly 165 organisations, and Ticketmaster, Santander and AT&T all appeared on the victim list. Attackers logged in with credentials harvested by infostealer malware, and they succeeded because those accounts had no multi-factor authentication switched on. The platform itself held up.
Investigators found no evidence that anyone breached Snowflake's own infrastructure, and the failures sat inside individual customer configurations. So a claim like the one attached to the ASOS data breach lands as plausible, and that history gives the threat its leverage. Plausible still falls short of confirmed, though. The burden of proof sits with the group making the claim, and it has not met that burden yet.
A Second ASOS Security Incident in Under Three Months
This is not the retailer's first problem of the year. ASOS detected unusual activity involving customer accounts on July 28, and a day later it found that an unauthorised third party had used login credentials sourced from outside the company. Notification letters went out on August 21.
A legal filing connected to that earlier ASOS data breach put the figure at roughly 138,828 individuals. Exposed fields included names, email addresses, delivery and billing addresses, telephone numbers and dates of birth. Attackers used credential stuffing. They tested stolen username and password pairs from unrelated leaks against ASOS accounts, betting that a fraction would still work.
Two incidents in under three months leave the same customer base exposed twice. Anyone caught in the July data breach now faces a second round of uncertainty at ASOS. Criminals building phishing lists get to cross-reference both sets, which makes any follow-on approach look better informed. Better informed means more convincing.
What ASOS Customers Should Do Now
Ignore the rogue notification, and do not open the link it carried. Nobody has explained where that link pointed, and a destination chosen by an extortion group deserves no clicks regardless. The app itself still works. ASOS has not asked anyone to uninstall it.
Treat incoming messages with suspicion for the next few weeks. Names, email addresses and phone numbers give criminals enough to build convincing phishing, and a data breach in the news hands them a ready-made pretext. ASOS makes a credible name to impersonate. The company will not ask for passwords or card details by email, text or phone.
Change the ASOS password if it appears anywhere else. Enable multi-factor authentication wherever the option exists. The July credential stuffing attack worked because people reuse passwords across unrelated services, and attackers know it. A password manager removes that problem, because nobody has to memorise anything.
What Businesses Should Take From the ASOS Data Breach
Marketing and engagement platforms sit outside most security reviews. They hold customer lists, and they hold the authority to speak to every name on those lists. Inventory every vendor with that reach. Scope its API keys to the minimum the job needs, and rotate those keys on a schedule rather than after an incident forces the question.
Build an incident communication plan that survives losing your own channels. ASOS warned customers about a hostile notification using the very app that had delivered it, which worked only because the ASOS data breach ended where it did. A longer-lived foothold would have stripped the retailer of every trusted route to its customers, right at the moment it needed one. Plan for the version where it does not end there.
The ASOS data breach fits a pattern running through retail this year. Attackers reach customer records through suppliers, integrations and communication tools, and they leave the core platform alone. Third-party access deserves the same scrutiny as production infrastructure. Customers see one brand and one app, so they hold that brand responsible for everything that arrives through it.
Subscribe to receive the latest blog posts to your inbox every week.