

CenterPoint Energy Confirms Data Breach Exposing Customer Info
CenterPoint Energy has confirmed a data breach affecting some of its customers, after a threat actor leaked records allegedly taken from the Houston-based utility. The company disclosed the incident in a Form 8-K filed with the U.S. Securities and Exchange Commission on September 14, 2026. It has not revealed the number of victims or the data involved. The attacker, however, claims to hold 7.49 million records.
CenterPoint supplies electricity and natural gas to roughly 7 million metered customers across Texas, Indiana, Minnesota, and Ohio. Its power and gas services kept running without interruption, so the damage centers on customer data. Even so, the size of the claimed leak leaves millions of households waiting for answers while the investigation continues.
How CenterPoint Energy Responded to the Data Breach
CenterPoint learned of the incident in early September, when a third party posted online that it held the company's customer information. The utility activated its incident response procedures, brought in outside cybersecurity specialists, and added protections to its systems. It also reported the incident to law enforcement and regulators.
CenterPoint Energy's investigation into the data breach has since confirmed that an unauthorized party reached customer information through an external-facing system. However, the filing leaves out the scope, the data types, and the attacker's identity. When asked about the attacker's claims, the company simply pointed back to its SEC disclosure.
The utility says it will notify affected customers and regulatory authorities as the law requires. It does not expect the incident to materially affect its business or financial condition. It also expects its cyber insurance to offset part of the response costs.
What the Attacker Claims to Have Stolen
The threat actor behind the leak uses the alias "4d722e4d656f77" and first came forward earlier this month. At that point, the actor said they had taken 7.49 million customer records from CenterPoint and later published the data online. The actor claims the company ignored their messages and treated the contact as a joke, which prompted the release.
The allegedly stolen records include customer names, phone numbers, service and billing addresses, account numbers, and billing amounts. The attacker also claims the files contain partial Social Security numbers. Other descriptions of the dataset mention email addresses, payment details, and driver's license information. Nobody has independently verified these fields.
CenterPoint Energy has not confirmed the record count or the authenticity of the files linked to the data breach. Until it does, the 7.49 million figure remains the attacker's own number.
An API Without Basic Protections
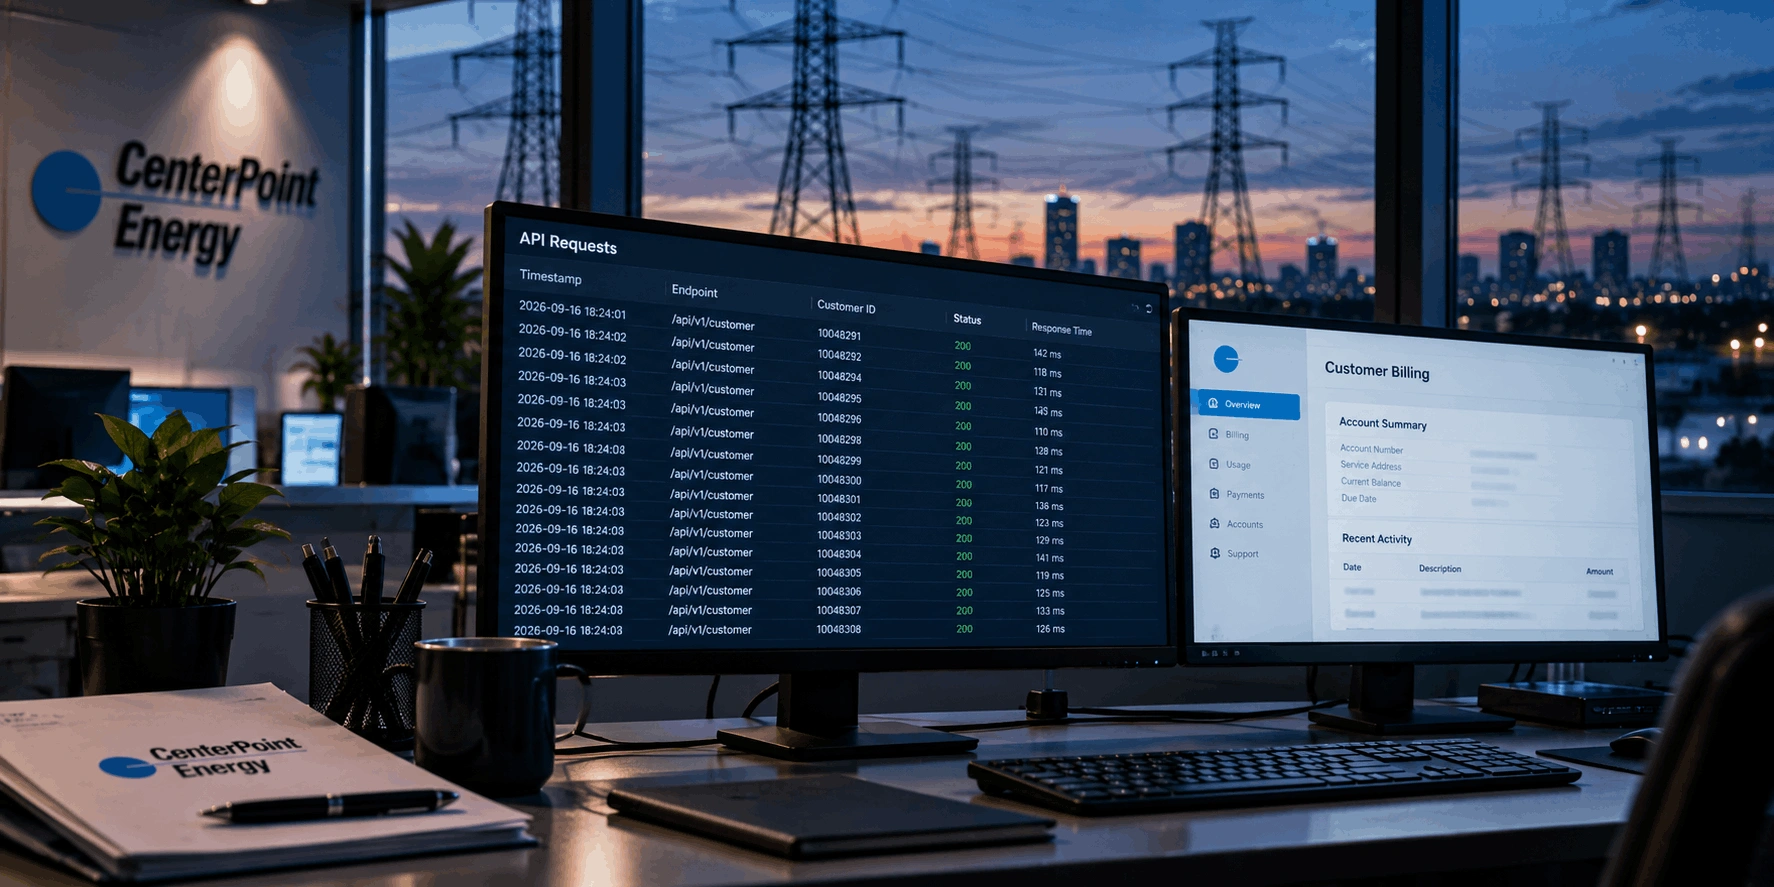
The attacker describes a simple method. They say they cycled through millions of customer IDs on a public CenterPoint API, pulling one record at a time. The interface allegedly lacked rate limiting, web application firewall protection, and other controls against automated access.
If accurate, this points to an enumeration attack, a form of broken access control. It needs no malware and no stolen passwords. An attacker only needs a predictable identifier and an endpoint that never checks who is asking, or how often.
The claim fits the company's own reference to an external-facing system. Still, CenterPoint Energy has not described the technical cause of the data breach in any public statement so far.
Lawsuits Arrive Before Notification Letters
Law firms have already filed several proposed class actions in federal court on behalf of potentially affected customers. The complaints allege the data breach at CenterPoint Energy took place between August 17 and September 1, 2026. Those cases landed before the company had named a single affected customer or described the stolen data.
This is also not the first time CenterPoint Energy has dealt with a data breach. Last year, the company investigated a separate incident tied to a 2023 attack. In that case, hackers took customer information through a widely used file-sharing platform. A second exposure within a few years will likely draw closer attention from regulators and plaintiffs alike.
What Affected Customers Should Watch For
Partial Social Security numbers exposed in a data breach like CenterPoint Energy's still carry real risk when paired with names, addresses, and account details. Criminals can use that mix to pass identity checks, open fraudulent accounts, or craft convincing scams.
Utility customers make an easy target for impersonation because nearly every household expects a regular bill. A scammer who quotes a real account number or billing amount can make a fake shutoff warning look genuine. Any CenterPoint Energy customer who gets an urgent payment demand citing the data breach should call the number on an official bill first.
Customers in the four affected states can also act now. A credit freeze with the three major bureaus blocks new accounts opened in their name. Regular reviews of bank statements and credit reports help catch misuse early. Multi-factor authentication also protects online utility and banking accounts.
Why Public APIs Keep Exposing Customer Data
For businesses, the alleged method matters more than the headline figure. Public APIs connect customer portals, mobile apps, and billing systems, so they often sit directly in front of sensitive records. If an endpoint accepts sequential IDs without authorization checks or request limits, a basic script can harvest its data at scale.
The fixes are well established. Organizations should enforce object-level authorization on every request, apply rate limiting, and place public APIs behind a web application firewall. Monitoring for bursts of sequential requests from one source can also flag enumeration before millions of records leave the network.
What Comes Next
CenterPoint's investigation remains open. The full scope of the data breach at CenterPoint Energy should become clearer once customer notifications go out and state regulators receive their filings. Until then, customers across all four states should assume their details may be circulating and stay alert for targeted scams.
For other utilities and service providers, the incident carries a plain lesson. A public API with no limits can undo much of themsecurity work built around it.
Subscribe to receive the latest blog posts to your inbox every week.