

Sweden Hits Miljödata With GDPR Fine Over 2.2 Million Breach
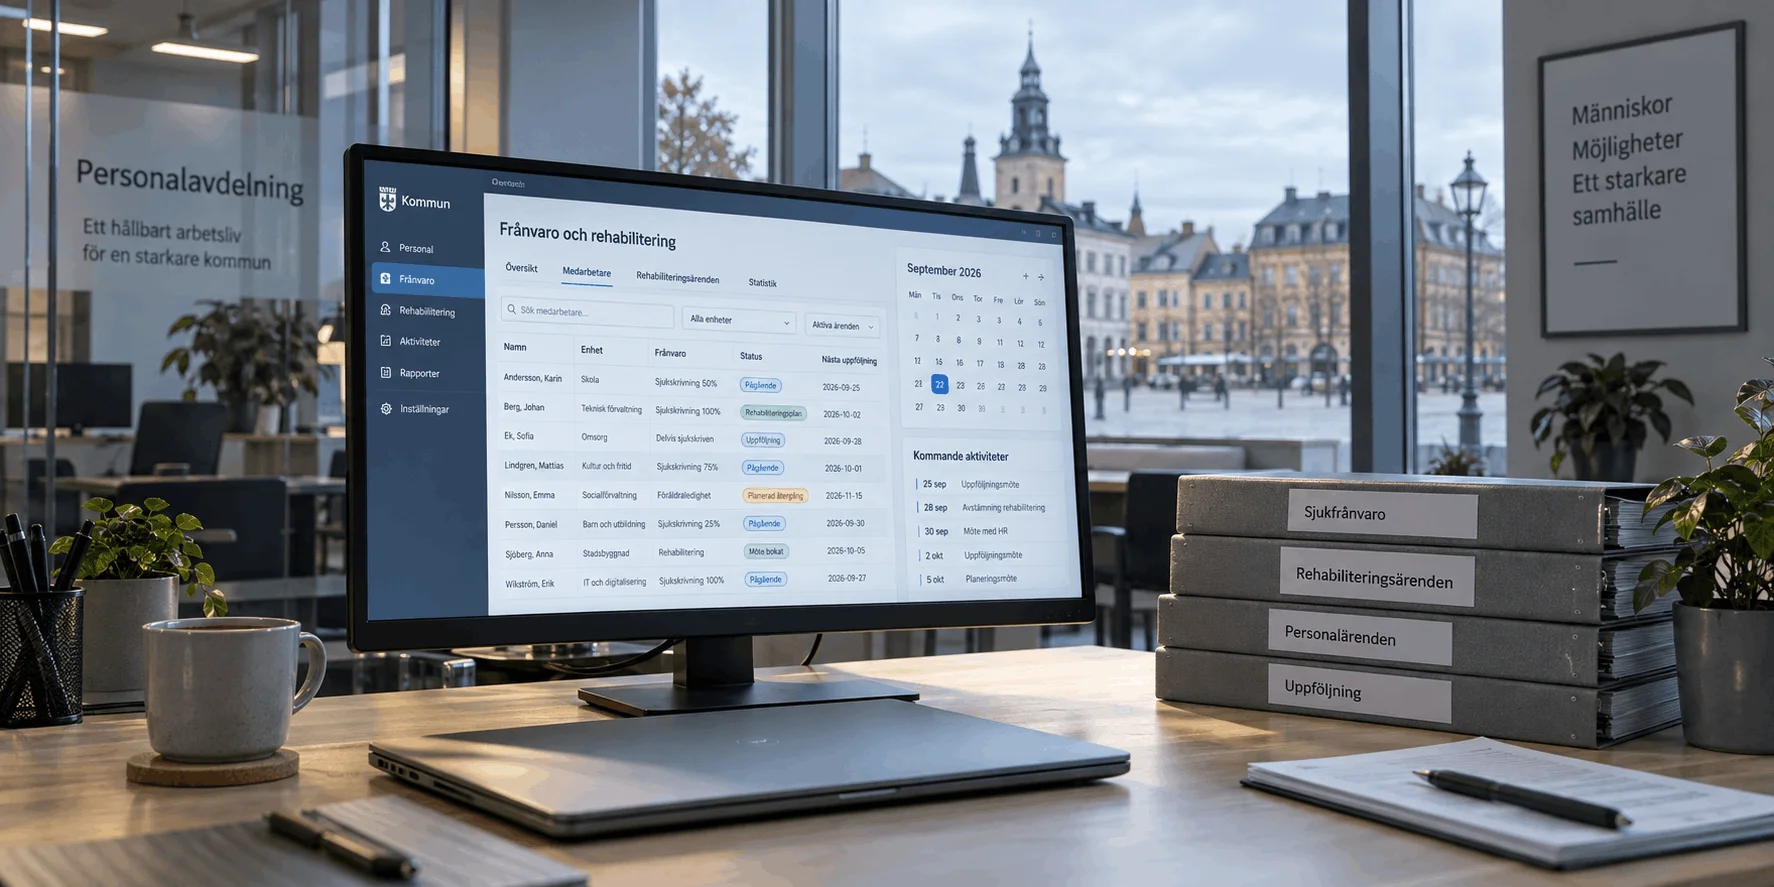
Sweden's data protection authority has issued Miljödata a GDPR fine of SEK 1.8 million, roughly $183,000. The penalty follows a 2025 cyberattack on the HR software supplier that exposed personal data belonging to 2.2 million people. The regulator, IMY, concluded that the company acted negligently and failed to protect the sensitive records it held. Those records included sick leave details, rehabilitation cases, and incidents involving school pupils.
IMY announced the GDPR fine against Miljödata on 22 September, closing a 10-month investigation into one of Sweden's largest data leaks. IMY is also still examining public bodies that relied on the company's systems, so further penalties remain possible. For employers and software vendors across Europe, the ruling offers a rare look at the specific security gaps a regulator will punish.
Why Miljödata Received a GDPR Fine
IMY identified two specific failures. First, the company did not run adequate checks when it installed new software. Second, it had no automated, real-time monitoring in place to detect intrusions or suspicious activity on its systems.
The regulator found that these shortcomings fell below the level of technical and organizational security the data demanded. Miljödata processed national identity numbers alongside health-related information, so the bar for protection sat high. IMY ruled that the gaps breached Article 32(1) of the GDPR, which requires security measures appropriate to the risk.
IMY also judged that Miljödata acted negligently, and that finding formed the basis for the GDPR fine. Director General Eric Leijonram said the lapses allowed a threat actor to obtain data covering a large share of Sweden's population. He urged other organizations to study the decision and review how they secure the personal data under their control.
How the 2025 Attack Unfolded
The events that led to Miljödata receiving a GDPR fine began on 20 August 2025, when attackers breached the company's network. Miljödata detected the ransomware attack three days later. Within days, municipalities, universities, and private employers lost access to core HR functions.
The attackers targeted Adato, a system for managing sick leave and rehabilitation, and Novi, a tool for HR case notes. Employers use both platforms to handle some of the most sensitive information they hold on staff. That includes medical certificates, rehabilitation plans, and work injury reports.
A group calling itself DataCarry claimed responsibility and demanded 1.5 Bitcoin, worth about $168,000 at the time. The group listed Miljödata on its leak site on 13 September and published the stolen data a day later. The leak contained personal identity numbers, contact details, and records on sick leave, rehabilitation, and school incidents involving minors.
Impact Beyond the Public Sector
Private companies felt the fallout too. Scandinavian airline SAS and mining group Boliden were among roughly 25 businesses affected through their use of Miljödata's platforms. Volvo Group North America later notified employees that the breach exposed their names and Social Security numbers.
A Supplier Breach With National Reach
Miljödata's customer base explains the scale of the incident. A majority of Sweden's municipalities used its systems, along with several regions, government agencies, and many private firms. One compromise at a single vendor therefore exposed staff data from hundreds of employers at once.
That concentration now carries regulatory consequences beyond the supplier. IMY has opened separate reviews into two municipalities and one region linked to the attack. Those reviews remain ongoing, so Miljödata may not be the only party to face a GDPR fine over the incident.
Under GDPR, organizations that hand personal data to a processor remain responsible for choosing suppliers that can protect it. A controller that fails to vet a vendor's security, or to set clear contractual requirements, can face scrutiny of its own.
What the Decision Means for Other Organizations
At SEK 1.8 million, the GDPR fine imposed on Miljödata sits far below the regulation's ceiling. Violations of Article 32 can draw fines of up to €10 million or 2% of global annual turnover, whichever is higher. But the substance of the ruling matters more than the amount.
IMY tied its GDPR fine to two concrete control gaps at Miljödata, and both have well-established fixes. Organizations can verify the source, integrity, and permissions of new software before deployment. They can also add continuous monitoring that flags unusual logins, large data transfers, and unexpected system changes as they happen.
The decision also confirms that the type of data drives the expected level of protection. Companies that store health information or national identity numbers face a higher bar under Article 32. So security budgets and controls should reflect the sensitivity of the records, not just the size of the business.
What Affected Individuals Should Watch For
People whose data appeared in the leak face long-term risk, and the GDPR fine on Miljödata does nothing to reverse that exposure. Swedish personal identity numbers do not change, so criminals can reuse them for identity fraud years after a breach. Details about sick leave or rehabilitation also give scammers material for convincing, targeted phishing.
Affected individuals should treat unexpected calls, emails, or texts that mention their employment, health, or HR cases with caution. They should verify any such contact through official channels before sharing information. Checking credit reports for unfamiliar applications adds another layer of protection.
Enforcement Reaches the Supply Chain
The GDPR fine IMY issued to Miljödata puts a concrete cost on missing basic security controls. It also sends a clear signal to software suppliers that handle public sector data. Regulators will examine the specific safeguards a company had in place, and they will name the gaps publicly.
With reviews of the affected municipalities and region still underway, the full regulatory fallout from the 2025 attack has yet to play out. For any organization that relies on a third party to process sensitive data, the case makes vendor security a direct compliance concern.
Subscribe to receive the latest blog posts to your inbox every week.