

Vanderbilt University Ransomware Attack: BYOD Claims Data Theft
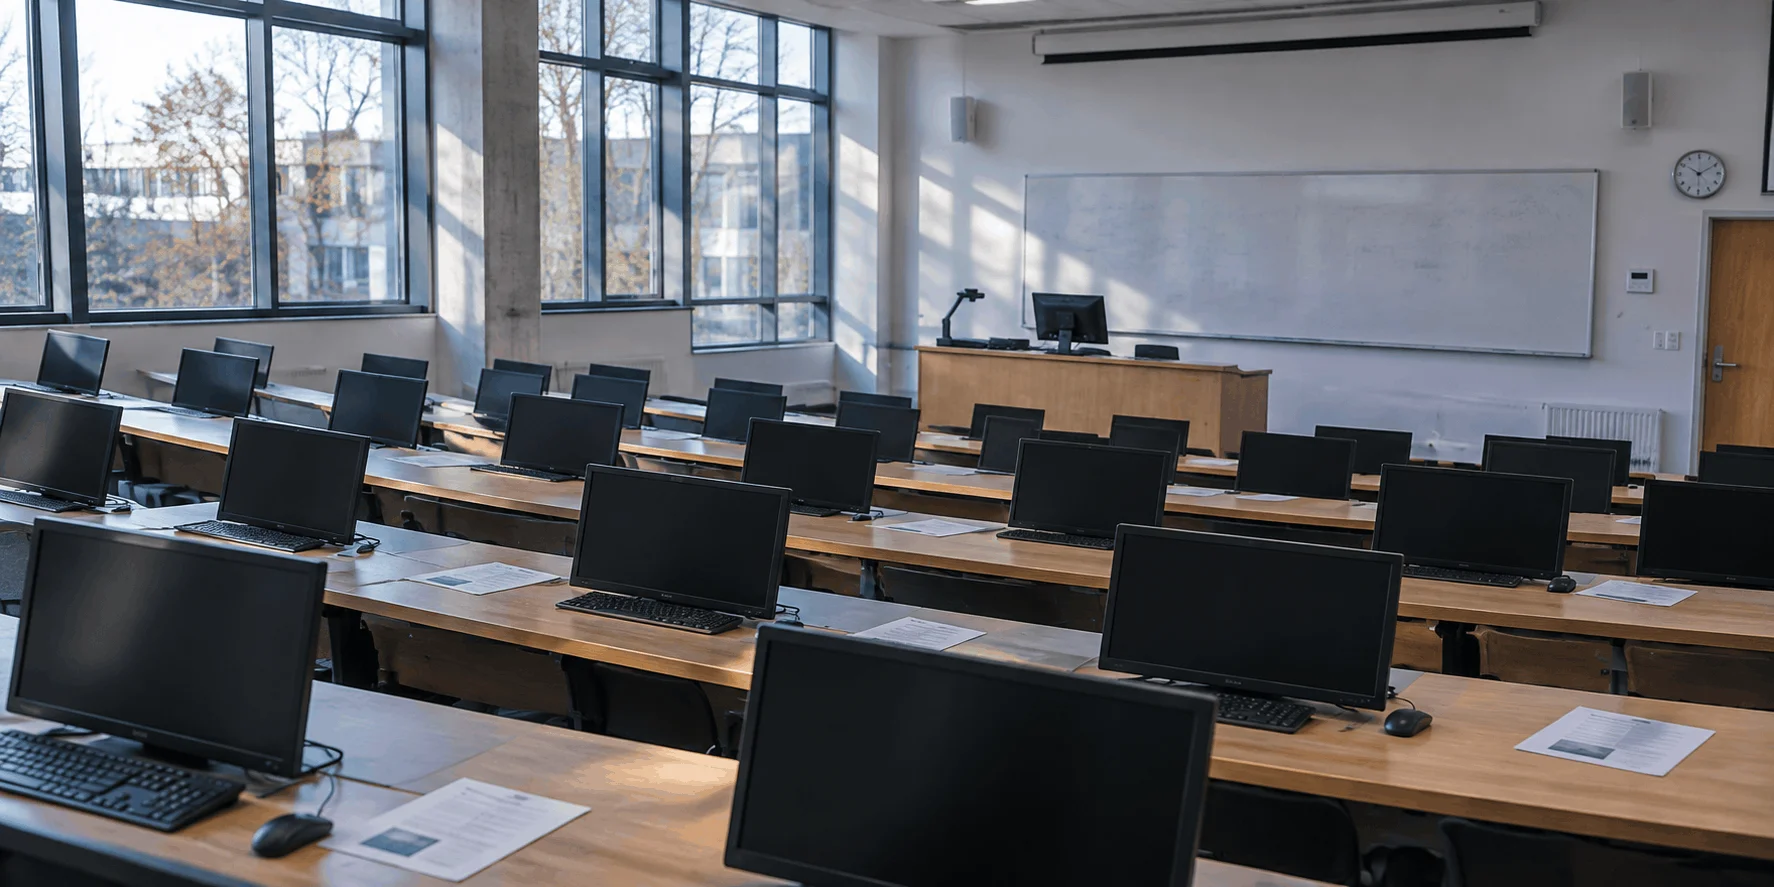
Vanderbilt University spent Monday telling its own community to turn off its computers. The instruction moved fast across the Nashville campus, and students traded Wi-Fi for phone hotspots while professors darkened their screens mid-lecture. Hours later, a crew calling itself BYOD claimed credit on its leak site, alleging it had encrypted the university’s databases and taken data on more than a million people. The Vanderbilt University ransomware attack now ranks among the most disruptive campus security incidents of the year, and the institution has yet to confirm what the attackers actually hold.
Why the Vanderbilt University Ransomware Attack Forced a Campus Shutdown
Vanderbilt confirmed a cybersecurity incident on Monday and said its IT team was investigating and working to contain the situation. The university asked every member of its community to shut down university devices, disconnect from campus Wi-Fi, and stay alert. It also told people to act immediately on anything unusual appearing on their machines.
Classes continued on schedule. Students switched to printed handouts to keep up with coursework, and departments improvised around systems they could no longer reach. Vanderbilt Health, which operates separately from the university, instructed its own employees to stay off university IT systems until further notice.
What a Shutdown Order Signals
Ordering an entire campus to power down is not a routine precaution. Responders reach for it when they suspect an attacker holds privileged access across the network and can reach endpoints at will. Disconnecting devices cuts that path, because ransomware spreads through live connections rather than dormant hardware.
The operational cost runs enormous, so nobody makes the call lightly. The instruction issued during the Vanderbilt University ransomware attack follows exactly that logic.
Inside the Claims Behind the Vanderbilt University Ransomware Attack
BYOD posted its listing on Monday, alleging it had taken the university’s entire estate alongside its research data. The post describes more than a million Social Security numbers, full names, email addresses, phone numbers, work addresses, job roles and birthdays. It also claims a complete takeover of Vanderbilt’s domain controller.
A ransom note named README_BYOD_31.txt appeared on affected screens. It links to the group’s leak site and routes negotiations through the SESSION encrypted messaging platform. Separate accounts describe files rewritten into an encoded .byod format and research data sitting unreachable on university systems. A video circulating on an anonymous student platform shows infected machines playing an audio warning, though nobody has verified where it came from.
Treat the Numbers as Allegations
None of this carries confirmation. Vanderbilt has not said data left its network, has not named BYOD, and has not described any encryption. Extortion crews inflate figures because inflated figures apply pressure, so the numbers attached to the Vanderbilt University ransomware attack belong in the allegation column until forensic work catches up. That work takes weeks, and sometimes months.
BYOD the Gang Versus BYOD the Policy
The group’s name collides with one of the most familiar acronyms in IT. Bring your own device describes letting staff use personal phones and laptops for work. The crew borrowed the term, but the ransomware attack on Vanderbilt University has no established connection to personal-device policy.
That distinction matters this week. Anyone searching for device-policy guidance will surface extortion headlines instead. Security teams reviewing their own rules should not read this incident as evidence against device programmes, because no public detail points to that entry route.
A Crew Working Through Higher Education
BYOD surfaced in September 2026 and built a victim list at speed. Public trackers count anywhere from five to eighteen listings, depending on how each one handles duplicate and update posts. Universities dominate the recent additions, and the ransomware attack on Vanderbilt University fits a pattern the group established weeks earlier.
On 26 October the crew claimed an intrusion at the University of New Mexico Health Sciences Center. That attack diverted ambulances and cancelled outpatient surgeries across the state. Clinical operations have since returned to normal.
Days later BYOD listed Michigan State University, claiming personal information on 1.03 million current and former students. Michigan State had already forced a campus-wide password reset in early October. Its investigation has so far found no evidence pointing to broader theft, and the work continues.
Targets Outside Education
The group also claimed Trump Mobile in October and published data on 3,615 customers, a leak that drew a letter from Senator Maggie Hassan to the company’s chief executive. Other listings name T-Mobile, recruitment firm eTeam, and IHG Hotels & Resorts.
After the New Mexico backlash, BYOD issued an unusual public statement claiming it had morals and offering compensation to affected patients. The University of New Mexico made no concessions and warned patients, students and staff against engaging with anyone claiming responsibility, including anyone offering payment.
Why Universities Keep Landing on Leak Sites
A research university runs one of the messiest networks in any sector. Tens of thousands of users rotate through every year, departments buy their own systems, and labs keep unpatched equipment running for experiments that span decades. Open collaboration sits at the heart of academic work, so the network resists the lockdown a bank would apply.
The data pays well too. Student records bundle Social Security numbers, financial aid details, campus clinic medical files and decades of alumni contact information. Research networks stack grant-funded intellectual property on top. Scale alone makes an incident like the Vanderbilt University ransomware attack lucrative for whoever gets in.
Budget pressure finishes the picture. Security spending competes with teaching and facilities, and lean internal teams face attackers who operate like businesses.
What Students and Staff Should Do Now
Anyone caught up in the Vanderbilt University ransomware attack should assume exposure and move before confirmation arrives. Waiting costs more than acting early.
- Freeze your credit with all three major bureaus. Freezes cost nothing and block new account openings, which is the primary risk once Social Security numbers circulate.
- Change reused passwords on any account sharing credentials with university systems, and turn on multi-factor authentication wherever it exists.
- Expect phishing. Attackers follow breach coverage closely, and messages posing as university IT will arrive.
- Check financial and benefit statements for activity you do not recognise.
Trust official university channels over social platforms for updates. The unverified video spreading this week demonstrates how quickly unconfirmed material fills the gap during an active incident.
What Comes After the Vanderbilt University Ransomware Attack
Vanderbilt faces a long recovery whatever investigators conclude. Rebuilding a compromised domain controller means rebuilding trust in every account and system sitting beneath it, and that process reaches far past the initial containment window. Breach notification duties will follow if personal data genuinely left the network, because Tennessee law sets deadlines for telling affected residents.
The sector now has a harder question in front of it. One group, barely two months old, has disrupted a hospital system, listed two major universities, and claimed over two million student records between them. Other institutions should study that pattern now, because campus networks will not get simpler and the people targeting them keep getting faster.
Subscribe to receive the latest blog posts to your inbox every week.